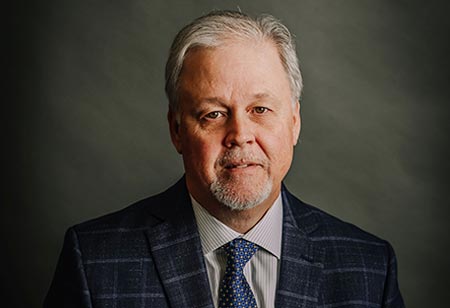
Tim Johns is a veteran IT professional with four decades of overall experience, including 25 years in cybersecurity. He began in the 1980s working with mainframe systems, later transitioning through client-server environments with deep experience across Microsoft and Novell platforms. In the late 1990s, he shifted his focus to IT security, building expertise in firewalls and emerging security architectures as the field matured. Over time, he specialized in cybersecurity governance and compliance, working extensively with frameworks including ISO 27001, ISO 31000, ISO 42001 and the NIST Cybersecurity Framework. His experience spans highly regulated environments such as healthcare and banking, where he supported physicians, attorneys and C-suite leaders with security, risk and compliance initiatives.